Automotive software development has become more structured as vehicles depend on software for increasingly important functions. Along with that growth, engineering teams often encounter two standards that appear together in automotive projects: Automotive SPICE (ASPICE) and ISO 26262.
Because both involve disciplined development, documentation, requirements, verification, and engineering processes, it is easy to assume that they serve the same purpose.
They do not.
A simple way to look at the difference is:
ASPICE asks: How well is the development process being performed?
ISO 26262 asks: How are safety risks from malfunctioning electrical and electronic systems being addressed?
ASPICE is primarily concerned with process capability and process improvement, while ISO 26262 is concerned with functional safety assurance.
The two can overlap significantly in an automotive software project, and engineering teams often need to address both. The practical challenge is not treating them as two completely separate activities, but understanding where their expectations connect and building a development process that supports both.
This article explains the difference between ASPICE and ISO 26262, where they overlap, how combined assessments work, and what the relationship means for engineering teams.
What Is ASPICE?
Automotive SPICE, commonly called ASPICE, is a process assessment framework used to evaluate the capability of development processes in automotive software and systems engineering.
It looks at how an organization performs engineering activities and whether those activities are defined, planned, managed, executed, and improved in a controlled way.
In simple terms, ASPICE is less about asking whether a particular product is safe and more about asking whether the organization has a repeatable and effective development process.
ASPICE can cover areas such as:
- Requirements analysis
- System architecture
- Software requirements analysis
- Software architecture
- Software construction
- Software integration
- Software testing
- System integration
- Verification
- Validation
- Configuration management
- Change management
- Problem resolution
For example, imagine an automotive supplier developing software for an electronic control unit.
An ASPICE-focused assessment may examine questions such as:
- Are customer requirements properly analyzed?
- Are software requirements derived and documented?
- Are requirements linked to architecture and testing?
- Are reviews performed?
- Are changes controlled?
- Are problems recorded and resolved?
- Can the team demonstrate that its development process is consistently followed?
The focus is on the development process and its capability.
What Is ISO 26262?
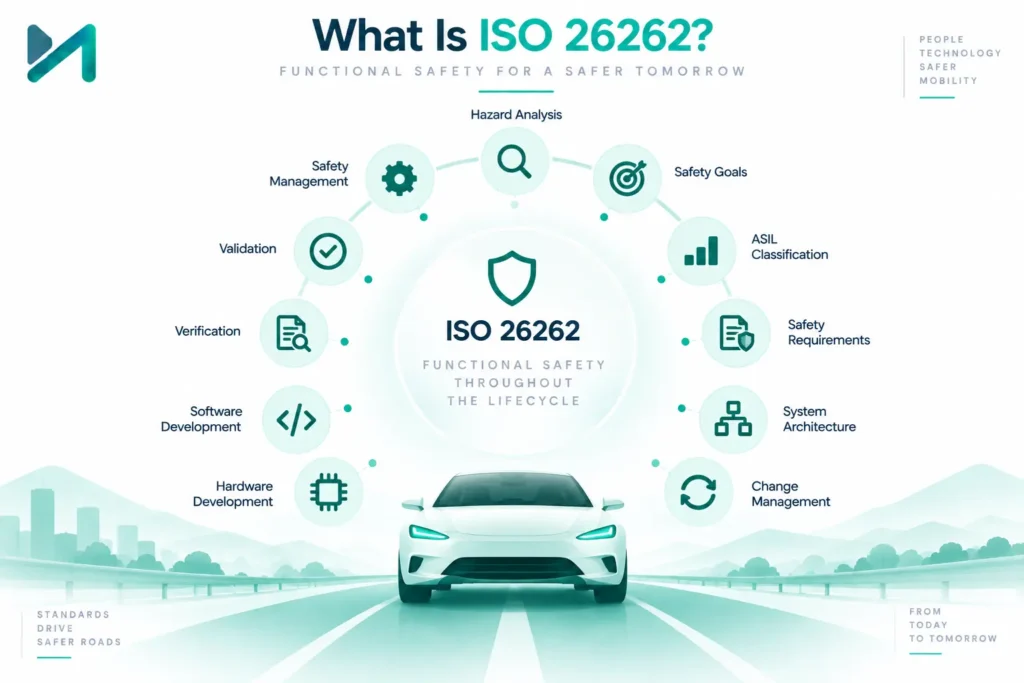
ISO 26262 is the international standard for functional safety of electrical and electronic systems in road vehicles.
Its purpose is different from ASPICE.
ISO 26262 addresses the risks associated with malfunctioning behavior of electrical and electronic systems and establishes a framework for managing functional safety throughout the product lifecycle.
It covers activities from the early concept phase through development, production, operation, service, and decommissioning.
Functional safety can involve:
- Hazard analysis and risk assessment
- Safety goals
- ASIL classification
- Safety requirements
- System architecture
- Hardware development
- Software development
- Verification
- Validation
- Safety management
- Configuration and change management
For example, suppose software controls a function that could contribute to a hazardous situation if it malfunctions.
ISO 26262 requires the organization to consider the associated risk and establish appropriate safety measures.
If you want to understand functional safety before comparing it with ASPICE, our guide on What Is Functional Safety? provides a practical introduction to the concept and the role of ISO 26262.
ASPICE vs ISO 26262: The Core Difference
The easiest way to understand the difference is to look at their primary objectives.
Area | ASPICE | ISO 26262 |
Primary focus | Development process capability | Functional safety |
Main concern | How engineering work is performed | How safety risks are addressed |
Typical context | Automotive systems and software development | Safety-related automotive electrical and electronic systems |
Key focus | Process definition, execution, assessment, and improvement | Risk reduction, safety lifecycle, and safety assurance |
Requirements | Requirements analysis and management | Safety requirements and their allocation |
Testing | Verification and validation processes | Verification and validation of safety-related requirements |
Change management | Controlled engineering changes | Controlled changes with consideration of safety impact |
Assessment | Process capability assessment | Safety lifecycle and work product evidence |
Outcome | Evidence of process capability | Evidence supporting functional safety |
The important thing is that ASPICE does not replace ISO 26262, and ISO 26262 does not replace ASPICE.
They address different concerns.
Process Improvement vs Safety Assurance
This is the most important distinction.
ASPICE: Process Improvement
ASPICE helps organizations understand whether their engineering processes are capable, consistent, and controlled.
For example, an organization may discover through an ASPICE assessment that:
- Requirements are not consistently reviewed.
- Traceability is incomplete.
- Testing activities are not sufficiently planned.
- Changes are not consistently documented.
- Software architecture decisions are not adequately recorded.
The organization can then improve those processes.
The emphasis is on making engineering development more predictable and repeatable.
ISO 26262: Safety Assurance
ISO 26262 starts with a different question:
What could happen if this electrical or electronic system malfunctions?
The organization then works through safety analysis, safety goals, requirements, architecture, implementation, verification, and validation to address those risks.
For example, if a software function contributes to a safety-related vehicle function, the team needs to understand what could happen if that function fails and establish appropriate safety measures.
A Simple Example
Imagine a software team developing an electronic braking-related function.
ASPICE perspective:
Are requirements properly defined, reviewed, traced, implemented, and tested using a controlled development process?
ISO 26262 perspective:
What hazards could result if this function malfunctions, what safety requirements are needed, and how can the associated risks be addressed?
The same engineering activity may therefore provide evidence relevant to both, but the reason for looking at it is different.
Where ASPICE and ISO 26262 Overlap
Although their objectives differ, there is considerable overlap between the two.
This is especially visible in software development activities.
Both can involve:
- Requirements management
- Requirements traceability
- Architecture
- Verification
- Validation
- Configuration management
- Change management
- Documentation
- Reviews
- Defect management
- Project planning
- Engineering evidence
This overlap is one reason automotive organizations often address ASPICE and ISO 26262 together.
For example, requirements traceability can support both frameworks.
An engineering team may have a chain such as:
Customer Requirement → System Requirement → Software Requirement → Architecture → Implementation → Test
From an ASPICE perspective, this demonstrates that the development process is connecting requirements with engineering activities.
From an ISO 26262 perspective, safety-related requirements can use similar relationships to demonstrate how safety objectives are translated into implementation and verification.
The evidence may overlap, but the purpose of the evidence is not necessarily identical.
Requirements Management Is Where the Two Often Meet
Requirements are a good example of how ASPICE and ISO 26262 can work together.
Consider a safety-related requirement:
The software shall detect an invalid sensor condition and initiate the defined fault response within the specified time.
From an ASPICE perspective, the team may need to demonstrate that the requirement was:
- Properly analyzed
- Reviewed
- Allocated
- Traced
- Implemented
- Verified
From an ISO 26262 perspective, the team may also need to demonstrate that the requirement supports the relevant safety objective and that the required safety behavior has been appropriately developed and verified.
This is why requirements management becomes so important in automotive engineering.
If requirements are scattered across spreadsheets, documents, emails, and separate testing systems, maintaining these relationships becomes difficult.
A connected lifecycle approach can make the overlap between process and safety activities much easier to manage.
Where They Differ
Despite the overlap, ASPICE and ISO 26262 should not be treated as interchangeable.
ASPICE focuses on:
How the organization develops the product.
It evaluates the capability and effectiveness of development processes.
ISO 26262 focuses on:
How the organization manages functional safety risks.
It establishes a safety lifecycle and activities for addressing risks associated with malfunctioning behavior.
This distinction matters when planning engineering activities.
A team could have a well-defined development process and still need to address functional safety separately.
Similarly, having safety-related activities does not automatically mean the organization’s broader development processes have the level of capability expected in an ASPICE assessment.
How the Two Standards Work Together
Rather than treating ASPICE and ISO 26262 as competing frameworks, organizations can use them together.
A practical relationship might look like this:
ASPICE provides the development process foundation
↓
ISO 26262 adds functional safety requirements to that development context
↓
Engineering teams execute development and safety activities together
↓
Traceability and evidence connect the activities
For example:
1. ASPICE establishes a disciplined requirements process.
2. ISO 26262 introduces safety-related requirements and safety activities.
3. Engineering teams develop and verify the software.
4. Traceability connects safety requirements to implementation and testing.
5. Process evidence and safety evidence are maintained throughout development.
This approach reduces unnecessary duplication.
What Is a Combined Assessment Approach?
Automotive organizations may need to demonstrate both process capability and functional safety practices.
A combined approach does not mean that ASPICE and ISO 26262 become one standard.
Instead, organizations can identify the areas where their activities and evidence overlap.
For example, a development process may already include:
- Requirements reviews
- Architecture reviews
- Verification
- Change management
- Configuration management
- Traceability
The organization can then identify which of those activities also support its functional safety process.
The benefit is practical: teams do not have to create entirely separate processes for every requirement.
However, shared evidence should only be used where it genuinely satisfies the relevant expectations. One document or activity should not automatically be assumed to satisfy both frameworks.
What Does a Combined Approach Look Like in Practice?
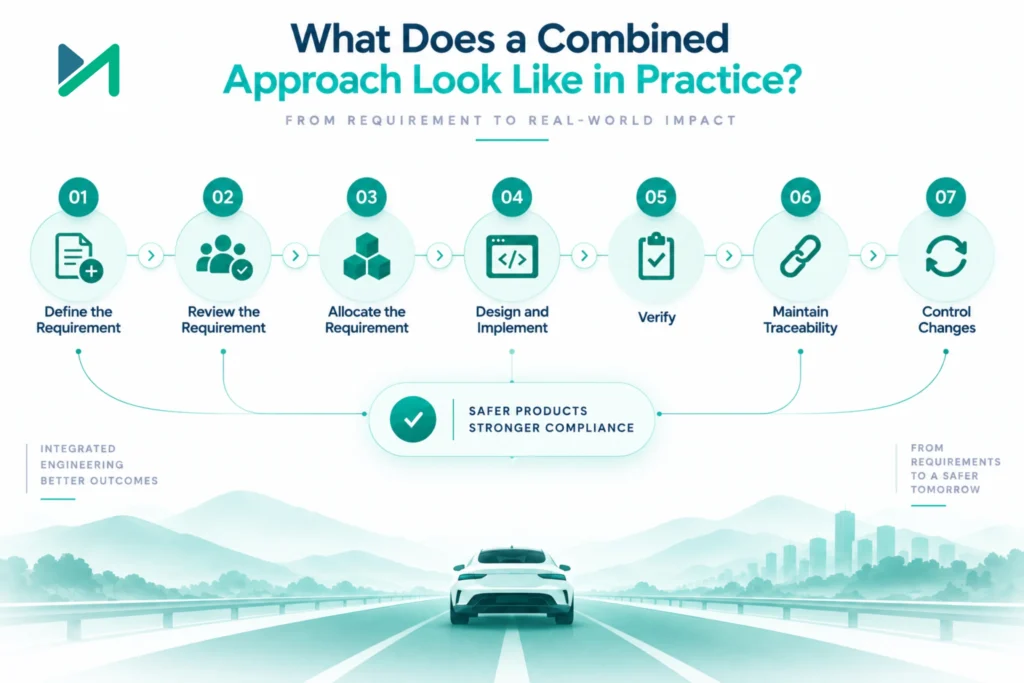
Consider a software requirement that is associated with a safety-related function.
The engineering process could look like:
Step 1: Define the Requirement
The requirement is created and linked to its source.
Step 2: Review the Requirement
The appropriate engineering stakeholders review and approve it.
Step 3: Allocate the Requirement
The requirement is assigned to the relevant software component.
Step 4: Design and Implement
The development team creates the appropriate architecture and implementation.
Step 5: Verify
A test case is linked to the requirement and the verification result is recorded.
Step 6: Maintain Traceability
The requirement remains connected to its source, implementation, and verification evidence.
Step 7: Control Changes
If the requirement changes, the team performs impact analysis and updates affected artifacts.
The same workflow can contribute to a more controlled ASPICE development process while also supporting the traceability and evidence needs associated with functional safety.
Practical Implications for Engineering Teams
For engineering teams, the biggest difference is not simply which standard applies.
The bigger question is:
How do we build a development process that can support both without creating unnecessary duplication?
Several practical considerations matter.
1. Define Requirements Clearly
Requirements should be understandable, specific, and verifiable.
Safety-related requirements also need to reflect the relevant safety objectives and constraints.
2. Maintain Traceability
Teams should be able to connect requirements to:
- Sources
- Architecture
- Implementation
- Tests
- Defects
- Changes
- Approvals
This becomes increasingly important as projects become larger.
3. Control Changes
A change that looks small to a developer may affect safety behavior or downstream engineering work.
Impact analysis should therefore be part of the normal change process.
4. Keep Evidence Throughout Development
Do not wait until an assessment to reconstruct what happened.
Reviews, approvals, test results, changes, and traceability should be captured as the work happens.
5. Give Teams One Clear Process
Developers should not have to remember one workflow for ASPICE and a completely different workflow for ISO 26262 when the underlying engineering activity is the same.
Where practical, organizations should create a common development workflow and identify the additional safety activities that apply to relevant projects.
A Practical Example: Automotive ECU Development
Consider an ECU responsible for managing a vehicle function.
The team receives a high-level customer requirement.
Under an ASPICE-oriented process
The team would:
1. Analyze the customer requirement.
2. Create system requirements.
3. Derive software requirements.
4. Design the software architecture.
5. Implement the software.
6. Verify the implementation.
Maintain traceability and change records.
Under ISO 26262
The team would additionally consider:
1. What hazards could result from malfunction?
2. What safety goals apply?
3. What ASIL classification is relevant?
4. What safety requirements need to be derived?
5. What safety mechanisms are required?
6. How should the safety requirements be verified?
7. What evidence demonstrates that the safety objectives have been addressed?
Notice how the two approaches interact.
The engineering process provides the structure, while the functional safety process adds safety-specific considerations.
Tools Can Help Connect the Two
Managing ASPICE and ISO 26262 activities across spreadsheets and disconnected systems becomes difficult as projects grow.
A lifecycle management environment can help connect:
- Requirements
- Reviews
- Architecture
- Development
- Testing
- Changes
- Defects
- Baselines
- Compliance evidence
If you’re evaluating tools for this purpose, our guide on Functional Safety and Compliance Tools explains the capabilities engineering teams should consider.
Before selecting a tool, look at your current process. Where are requirements created? Where are they approved? Where do test results live? How are changes tracked? Can you identify the impact of a requirement change without manually checking several systems?
Those questions often reveal the real requirements for an ALM platform.
Building a Compliance-Ready Development Process
The goal should not be to create separate documentation simply because two frameworks are involved.
A better approach is to build a development process where evidence is created naturally as engineering work happens.
For example:
Requirement → Review → Design → Implementation → Verification → Approval → Evidence
When a requirement changes:
Change → Impact Analysis → Review → Implementation → Reverification → Updated Evidence
This approach makes the development process easier to manage while giving engineering and quality teams better visibility.
If your organization is working toward a more structured development process, our guide on compliance-ready software development explains how teams can build compliance activities into the software lifecycle rather than treating them as a separate exercise.
What Engineering Teams Should Do Differently
If your organization needs to address both ASPICE and ISO 26262, the practical steps are fairly straightforward.
Start with the development process
Document how requirements, architecture, development, testing, changes, and defects are currently managed.
Identify safety-related activities
Determine which products and functions require functional safety activities and where safety requirements enter the development lifecycle.
Map the overlap
Identify common activities such as requirements management, traceability, verification, change management, and configuration management.
Define additional safety controls
Where ISO 26262 introduces requirements beyond the normal development process, make those activities explicit.
Automate traceability where possible
Avoid relying on manually maintained spreadsheets for relationships that change frequently.
Maintain evidence continuously
Capture reviews, approvals, changes, verification results, and traceability as part of normal engineering work.
If your team is maintaining separate spreadsheets for ASPICE evidence and safety evidence, take a step back and map where the same engineering information is being recorded twice. That exercise often reveals opportunities to simplify the process.
How MicroGenesis Supports Connected Automotive Engineering Processes
ASPICE and ISO 26262 become much easier to manage when engineering teams can see how their requirements, development activities, testing, and changes are connected.
For example, when a safety-related requirement changes, the team should not have to manually search through multiple spreadsheets and documents to determine what needs to be reviewed. They should be able to identify the related requirements, engineering artifacts, tests, and approvals, then assess the impact before the change moves forward.
This is where a well-structured ALM environment becomes valuable.
MicroGenesis works with organizations to structure their engineering lifecycle around connected requirements, traceability, development, testing, change management, and compliance activities. The focus is on aligning the tools with the organization’s existing engineering process rather than forcing every team into the same workflow.
The right ALM approach should make engineering work easier to follow, not create another layer of administration. The objective is to give teams a reliable connection between what was required, what was developed, what was tested, and what changed.
Organizations looking to improve this connection can explore MicroGenesis ALM Services to understand how ALM can be structured around their engineering and compliance requirements.
For teams already working with IBM’s engineering tools, IBM Engineering Lifecycle Management provides a platform for managing connected engineering lifecycle activities, including requirements and traceability.
Conclusion
ASPICE and ISO 26262 are closely related in automotive development, but they are not the same thing.
The simplest distinction is:
ASPICE focuses on development process capability and improvement.
ISO 26262 focuses on functional safety and the management of risks associated with malfunctioning electrical and electronic systems.
They overlap in important areas such as:
- Requirements management
- Traceability
- Architecture
- Verification
- Validation
- Change management
- Configuration management
- Engineering evidence
This overlap gives automotive organizations an opportunity to build a combined development approach rather than maintaining completely separate processes.
The key is to understand what each framework expects, identify the activities they share, and then add the safety-specific controls required for functional safety.
For engineering teams, the goal is not simply to “pass ASPICE” or “be ISO 26262 compliant.” The more useful objective is to create a development process where quality, traceability, safety, and evidence are built into everyday engineering work.